Buy satoshifast.com ?
We are moving the project
satoshifast.com .
Are you interested in purchasing the domain
satoshifast.com ?
domain@kv-gmbh.de · 0541-91531010
Buy satoshifast.com ?
Who has disabled EFI Secure Boot and TPM?
EFI Secure Boot and TPM can be disabled by the user or system administrator. This may be done for various reasons, such as to install a non-secure boot operating system or to troubleshoot compatibility issues with certain hardware or software. Additionally, some organizations may disable these features as part of their security policies or to allow for greater flexibility in managing their systems. **
What is BitLocker TPM?
BitLocker TPM (Trusted Platform Module) is a security feature in Windows operating systems that uses a hardware component called TPM to provide enhanced protection for data stored on a computer's hard drive. TPM is a microchip that securely stores encryption keys, passwords, and other sensitive information to help protect against unauthorized access to the system. When BitLocker TPM is enabled, the encryption keys are securely stored in the TPM, making it more difficult for attackers to access the data even if they physically remove the hard drive from the computer. **


Similar search terms for Tpm
Top-Angebote
Products related to Tpm:
-
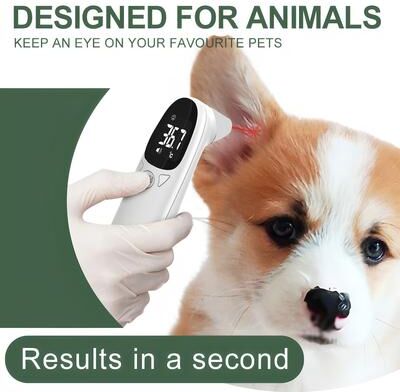
Happy Pet Pantry Veterinary Digital Thermometer For Pets & Livestock Fast Accurate Temperature Monitor Veterinary Digital Thermometer For Pets & Livestock Fast Accurate Temperature MonitorFeeling confident about your animal's health starts with accurate temperature checks. This veterinarygrade thermometer delivers fast, reliable readings for farmers, breeders, veterinarians, and pet owners who need quick results when every minute...36,97 $*Shipping: 0,00 $Secure redirect to the provider
-
Mason Cash Innovative Kitchen Mixing BowlThis Mason Cash mixing bowl has a capacity of 4 litres and features tilt support in the design and shape of the bowl. As the bowl is tilted, the indents in the outer surface of the bowl provided angled support when mixing and beating the contents of the bowl. The bowl is made from stoneware and is finished with a durable and hard wearing glaze. The Mason Cash mixing bowl is suitable for warming food in the microwave and is dishwasher safe for easy and convenient cleaning.24,50 £*Shipping: 3,50 £Secure redirect to the provider
-
Mason Cash Innovative Kitchen Lasagne DishThe Mason Cash Innovative Kitchen Lasagne Dish is made from stoneware which provides gradual and even heat distribution. A vented base also ensures optimal heat distribution whilst right angled corners and precision sizing accommodate most lasagne sheets without the need to break them down. Steep sides allow for higher layering and help distribute heat evenly. Mason Cash ovenware classics have been given the Innovative Kitchen treatment in this range. Carefully selected materials with innovative features that improve their performance for tastier results. The Mason Cash Innovative Kitchen Lasagne Dish measures H 7.3cm x W 31.5cm x D 20.5cm with a capacity of 2.5 litres.16,10 £*Shipping: 3,50 £Secure redirect to the provider


-
Can't you activate TPM?
Yes, TPM (Trusted Platform Module) can be activated on compatible devices through the device's BIOS settings. However, not all devices have TPM built-in, so it's important to check the device's specifications to see if TPM is available. Once activated, TPM provides hardware-based security features such as secure boot, device encryption, and key management to help protect sensitive data and ensure the integrity of the system. **
-
How do I activate TPM 2.0 and Secure Boot in Valorant?
To activate TPM 2.0 and Secure Boot in Valorant, you will need to access your computer's BIOS or UEFI settings. Restart your computer and press the designated key (often F2, F10, or Del) to enter the BIOS/UEFI. Once in the settings, navigate to the Security or Boot options and look for the TPM and Secure Boot settings. Enable TPM 2.0 and Secure Boot if they are not already activated, then save and exit the BIOS/UEFI. After making these changes, you should be able to play Valorant with TPM 2.0 and Secure Boot activated. **
-
Is TPM 2.0 and Secure Boot required for Windows 11? I have Windows 11, but TPM is disabled on my device.
Yes, TPM 2.0 and Secure Boot are required for Windows 11. These security features help protect the system from malware and other security threats. If TPM is disabled on your device, you may need to enable it in the BIOS settings to meet the Windows 11 system requirements. Additionally, you may also need to enable Secure Boot if it is not already enabled on your device. **
-
What exactly is TPM 2.0?
TPM 2.0, which stands for Trusted Platform Module 2.0, is a hardware-based security feature that provides a secure foundation for various security functions, such as encryption, authentication, and key management. It is a microcontroller that is typically integrated into computer systems to enhance security by securely storing sensitive information, such as encryption keys, digital certificates, and passwords. TPM 2.0 helps protect against various security threats, including unauthorized access, malware attacks, and data breaches, by providing a secure environment for sensitive data and cryptographic operations. **
How do I activate TPM?
To activate TPM (Trusted Platform Module) on your computer, you will need to access the BIOS or UEFI settings. Restart your computer and enter the BIOS/UEFI by pressing a specific key (usually F2, F10, or Del) during the boot-up process. Look for the TPM settings in the security or advanced settings section and enable TPM. Save the changes and exit the BIOS/UEFI settings. TPM should now be activated on your computer. **
How can one delete TPM?
To delete TPM (Trusted Platform Module) on a computer, you would need to access the computer's BIOS or UEFI settings. Once in the settings, you can navigate to the security or TPM section and find the option to clear or reset the TPM. This will remove any existing TPM data and settings from the computer. It's important to note that deleting TPM may have implications for the computer's security and functionality, so it should only be done if necessary and with caution. **
Top-Angebote
Products related to Tpm:
-
Asus TPM-SPI V2.0 Security TPM ModuleThe ASUS TPM SPI V2.0 Security Module is designed to enhance computer security by providing dedicated hardware based protection for compatible systems. It helps securely store encryption keys, digital certificates, passwords and other sensitive information. Using a 14-1 pin SPI interface, the module is designed for compatible ASUS motherboards and systems that support the TPM SPI standard. It provides a dedicated Trusted Platform Module solution for systems requiring hardware based security features. The module uses the Nuvoton NPCT750 security chip and complies with the Trusted Computing Group TPM 2.0 specification. This allows it to support security functions that help protect platform integrity and digital identities. Security certifications include Common Criteria EAL4+ and FIPS 140-2. The module also meets CE and RoHS compliance requirements, providing a certified solution for compatible computing platforms. The ASUS TPM SPI V2.0 is a compact internal security accessory designed for straightforward motherboard integration. Before installation, compatibility should be checked carefully because TPM SPI and TPM LPC modules use different pin definitions and are not interchangeable.15,99 £*Shipping: 0,00 £Secure redirect to the provider
-
Happy Pet Pantry Veterinary Digital Thermometer For Pets & Livestock Fast Accurate Temperature Monitor Veterinary Digital Thermometer For Pets & Livestock Fast Accurate Temperature MonitorFeeling confident about your animal's health starts with accurate temperature checks. This veterinarygrade thermometer delivers fast, reliable readings for farmers, breeders, veterinarians, and pet owners who need quick results when every minute...36,97 $*Shipping: 0,00 $Secure redirect to the provider
-
Who has disabled EFI Secure Boot and TPM?
EFI Secure Boot and TPM can be disabled by the user or system administrator. This may be done for various reasons, such as to install a non-secure boot operating system or to troubleshoot compatibility issues with certain hardware or software. Additionally, some organizations may disable these features as part of their security policies or to allow for greater flexibility in managing their systems. **
-
What is BitLocker TPM?
BitLocker TPM (Trusted Platform Module) is a security feature in Windows operating systems that uses a hardware component called TPM to provide enhanced protection for data stored on a computer's hard drive. TPM is a microchip that securely stores encryption keys, passwords, and other sensitive information to help protect against unauthorized access to the system. When BitLocker TPM is enabled, the encryption keys are securely stored in the TPM, making it more difficult for attackers to access the data even if they physically remove the hard drive from the computer. **
-
Can't you activate TPM?
Yes, TPM (Trusted Platform Module) can be activated on compatible devices through the device's BIOS settings. However, not all devices have TPM built-in, so it's important to check the device's specifications to see if TPM is available. Once activated, TPM provides hardware-based security features such as secure boot, device encryption, and key management to help protect sensitive data and ensure the integrity of the system. **
-
How do I activate TPM 2.0 and Secure Boot in Valorant?
To activate TPM 2.0 and Secure Boot in Valorant, you will need to access your computer's BIOS or UEFI settings. Restart your computer and press the designated key (often F2, F10, or Del) to enter the BIOS/UEFI. Once in the settings, navigate to the Security or Boot options and look for the TPM and Secure Boot settings. Enable TPM 2.0 and Secure Boot if they are not already activated, then save and exit the BIOS/UEFI. After making these changes, you should be able to play Valorant with TPM 2.0 and Secure Boot activated. **
Similar search terms for Tpm
-
Mason Cash Innovative Kitchen Mixing BowlThis Mason Cash mixing bowl has a capacity of 4 litres and features tilt support in the design and shape of the bowl. As the bowl is tilted, the indents in the outer surface of the bowl provided angled support when mixing and beating the contents of the bowl. The bowl is made from stoneware and is finished with a durable and hard wearing glaze. The Mason Cash mixing bowl is suitable for warming food in the microwave and is dishwasher safe for easy and convenient cleaning.24,50 £*Shipping: 3,50 £Secure redirect to the provider
-
Mason Cash Innovative Kitchen Lasagne DishThe Mason Cash Innovative Kitchen Lasagne Dish is made from stoneware which provides gradual and even heat distribution. A vented base also ensures optimal heat distribution whilst right angled corners and precision sizing accommodate most lasagne sheets without the need to break them down. Steep sides allow for higher layering and help distribute heat evenly. Mason Cash ovenware classics have been given the Innovative Kitchen treatment in this range. Carefully selected materials with innovative features that improve their performance for tastier results. The Mason Cash Innovative Kitchen Lasagne Dish measures H 7.3cm x W 31.5cm x D 20.5cm with a capacity of 2.5 litres.16,10 £*Shipping: 3,50 £Secure redirect to the provider
-
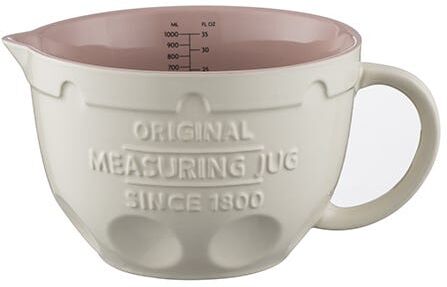
Mason Cash Innovative Kitchen 1L Measuring JugThe Mason Cash Innovative kitchen 1 litre measuring jug is a must have in the kitchen for baking large batches of ingredients. The stoneware bowl has a large handle providing a good grip when mixing the contents. The bowl features indentations on the exterior, which provides extra support when the bowl is tilted at an angle. The inside of the measuring bowl shows measurements in both millilitres and fluid ounces. Suitable for use in the microwave and dishwasher safe for easy and convenient cleaning, the measuring bowl is part of a matching collection.17,85 £*Shipping: 3,50 £Secure redirect to the provider
-
Mason Cash Innovative Kitchen 29cm Pie DishThe Mason Cash Innovative Kitchen Pie Dish is made from stoneware which provides gradual and even heat distribution. A vented base also ensures optimal heat distribution as do the steep sides of the dish. An embossed interior provides easy pastry release whilst the pastry anchor prevents pastry slumping. Mason Cash ovenware classics have been given the Innovative Kitchen treatment in this range. Carefully selected materials with innovative features that improve their performance for tastier results. The Mason Cash Innovative Kitchen Pie Dish measures H 5.5cm x W 28cm x D 28cm with a capacity of 2 litres.15,05 £*Shipping: 3,50 £Secure redirect to the provider
-
Is TPM 2.0 and Secure Boot required for Windows 11? I have Windows 11, but TPM is disabled on my device.
Yes, TPM 2.0 and Secure Boot are required for Windows 11. These security features help protect the system from malware and other security threats. If TPM is disabled on your device, you may need to enable it in the BIOS settings to meet the Windows 11 system requirements. Additionally, you may also need to enable Secure Boot if it is not already enabled on your device. **
-
What exactly is TPM 2.0?
TPM 2.0, which stands for Trusted Platform Module 2.0, is a hardware-based security feature that provides a secure foundation for various security functions, such as encryption, authentication, and key management. It is a microcontroller that is typically integrated into computer systems to enhance security by securely storing sensitive information, such as encryption keys, digital certificates, and passwords. TPM 2.0 helps protect against various security threats, including unauthorized access, malware attacks, and data breaches, by providing a secure environment for sensitive data and cryptographic operations. **
-
How do I activate TPM?
To activate TPM (Trusted Platform Module) on your computer, you will need to access the BIOS or UEFI settings. Restart your computer and enter the BIOS/UEFI by pressing a specific key (usually F2, F10, or Del) during the boot-up process. Look for the TPM settings in the security or advanced settings section and enable TPM. Save the changes and exit the BIOS/UEFI settings. TPM should now be activated on your computer. **
-
How can one delete TPM?
To delete TPM (Trusted Platform Module) on a computer, you would need to access the computer's BIOS or UEFI settings. Once in the settings, you can navigate to the security or TPM section and find the option to clear or reset the TPM. This will remove any existing TPM data and settings from the computer. It's important to note that deleting TPM may have implications for the computer's security and functionality, so it should only be done if necessary and with caution. **
* All prices are inclusive of VAT and, if applicable, plus shipping costs. The offer information is based on the details provided by the respective shop and is updated through automated processes. Real-time updates do not occur, so deviations can occur in individual cases. ** Note: Parts of this content were created by AI.